I'm Antonio Cebreiro Bernárdez, a computer engineer and cybersecurity consultant. I work freelance and remotely, under the ACBSEC brand, with companies of any location and size.
I support organisations on two fronts that usually go together: strategy and compliance —NIS2, ISO/IEC 27001, ENS, TISAX— and the technical projects that hold them up, mostly around the Microsoft ecosystem, information protection and data loss prevention. I have also built and led security teams from scratch.
I am also a co-founder of Usoarit alongside Anxo Pereira Fernández and Victoria Melissa Toledo Luna. At Usoarit we provide human resources consulting for technology companies.
This page sets out my full profile. If you're looking for the services or want to get in touch, that's on the home page.
Areas of expertise, certifications and frameworks
My professional background combines cybersecurity, information security, regulatory compliance, security architecture, technology and team leadership.
Cybersecurity and information security
My experience covers, among others, the following areas:
- Governance, risk and compliance (GRC).
- Cybersecurity strategy.
- Information security.
- Risk management and risk analysis.
- Security architecture.
- Cloud security.
- Identity and access management (IAM).
- Information protection.
- Data loss prevention (DLP).
- Microsoft Security.
- Zero Trust.
- Security culture and awareness.
- Industrial cybersecurity.
- Security in the automotive sector.
I work with Entra ID, Purview, Intune, Defender, CASB, Proofpoint, Zscaler and Nessus, as well as email security and social engineering.
Regulations, standards and frameworks
I work with the main frameworks and standards that organisations use to manage and improve their cybersecurity:
- ISO/IEC 27001 — information security management systems.
- Spain's National Security Framework (ENS).
- The NIS2 Directive and its cybersecurity and resilience requirements.
- TISAX — information security assessment for the automotive supply chain, based on the VDA ISA catalogue.
- CIS Controls and NIST CSF.
- Frameworks and good practice around governance, risk, compliance and security architecture.
Certifications and credentials
My main professional certifications and credentials include:
I also hold the UNECE R/155 · Automotive cybersecurity credential from Cybentia.
On top of that, specialised training in industrial cybersecurity, information security, Microsoft Security and data and information protection.
These certifications and credentials complement my professional experience on cybersecurity, compliance, architecture and information protection projects.
NIS2, ISO 27001 and ENS
A large part of my current work consists of helping organisations turn these requirements into concrete actions.
Depending on what each company needs, I work on:
Scope analysis, gap analysis, identification of obligations, risk assessment and roadmap definition.
Implementation and improvement of information security management systems, risk analysis, controls and audit preparation.
Situation analysis, gap identification and support throughout the compliance process.
Gap analysis against the VDA ISA catalogue, control definition and support in preparing for the assessment.
My aim is not to stop at interpreting a standard, but to help the organisation understand what applies to it, what it has to do, what it should prioritise and how to put it into practice.
If you want to check where you stand before talking to me, there's the NIS2 checklist —scope plus 16 controls— and the rest of the free tools. And if you'd rather read me first, I write on the blog about compliance, Microsoft security and supply chain.
Talks and outreach
I have spoken at industry events and universities, and appeared on Galician television. Selected talks:
- AMTEGA · CyberSecurity Next Gen Leaders
- CIBERECO · Basic Security Posture Management (BSPM)
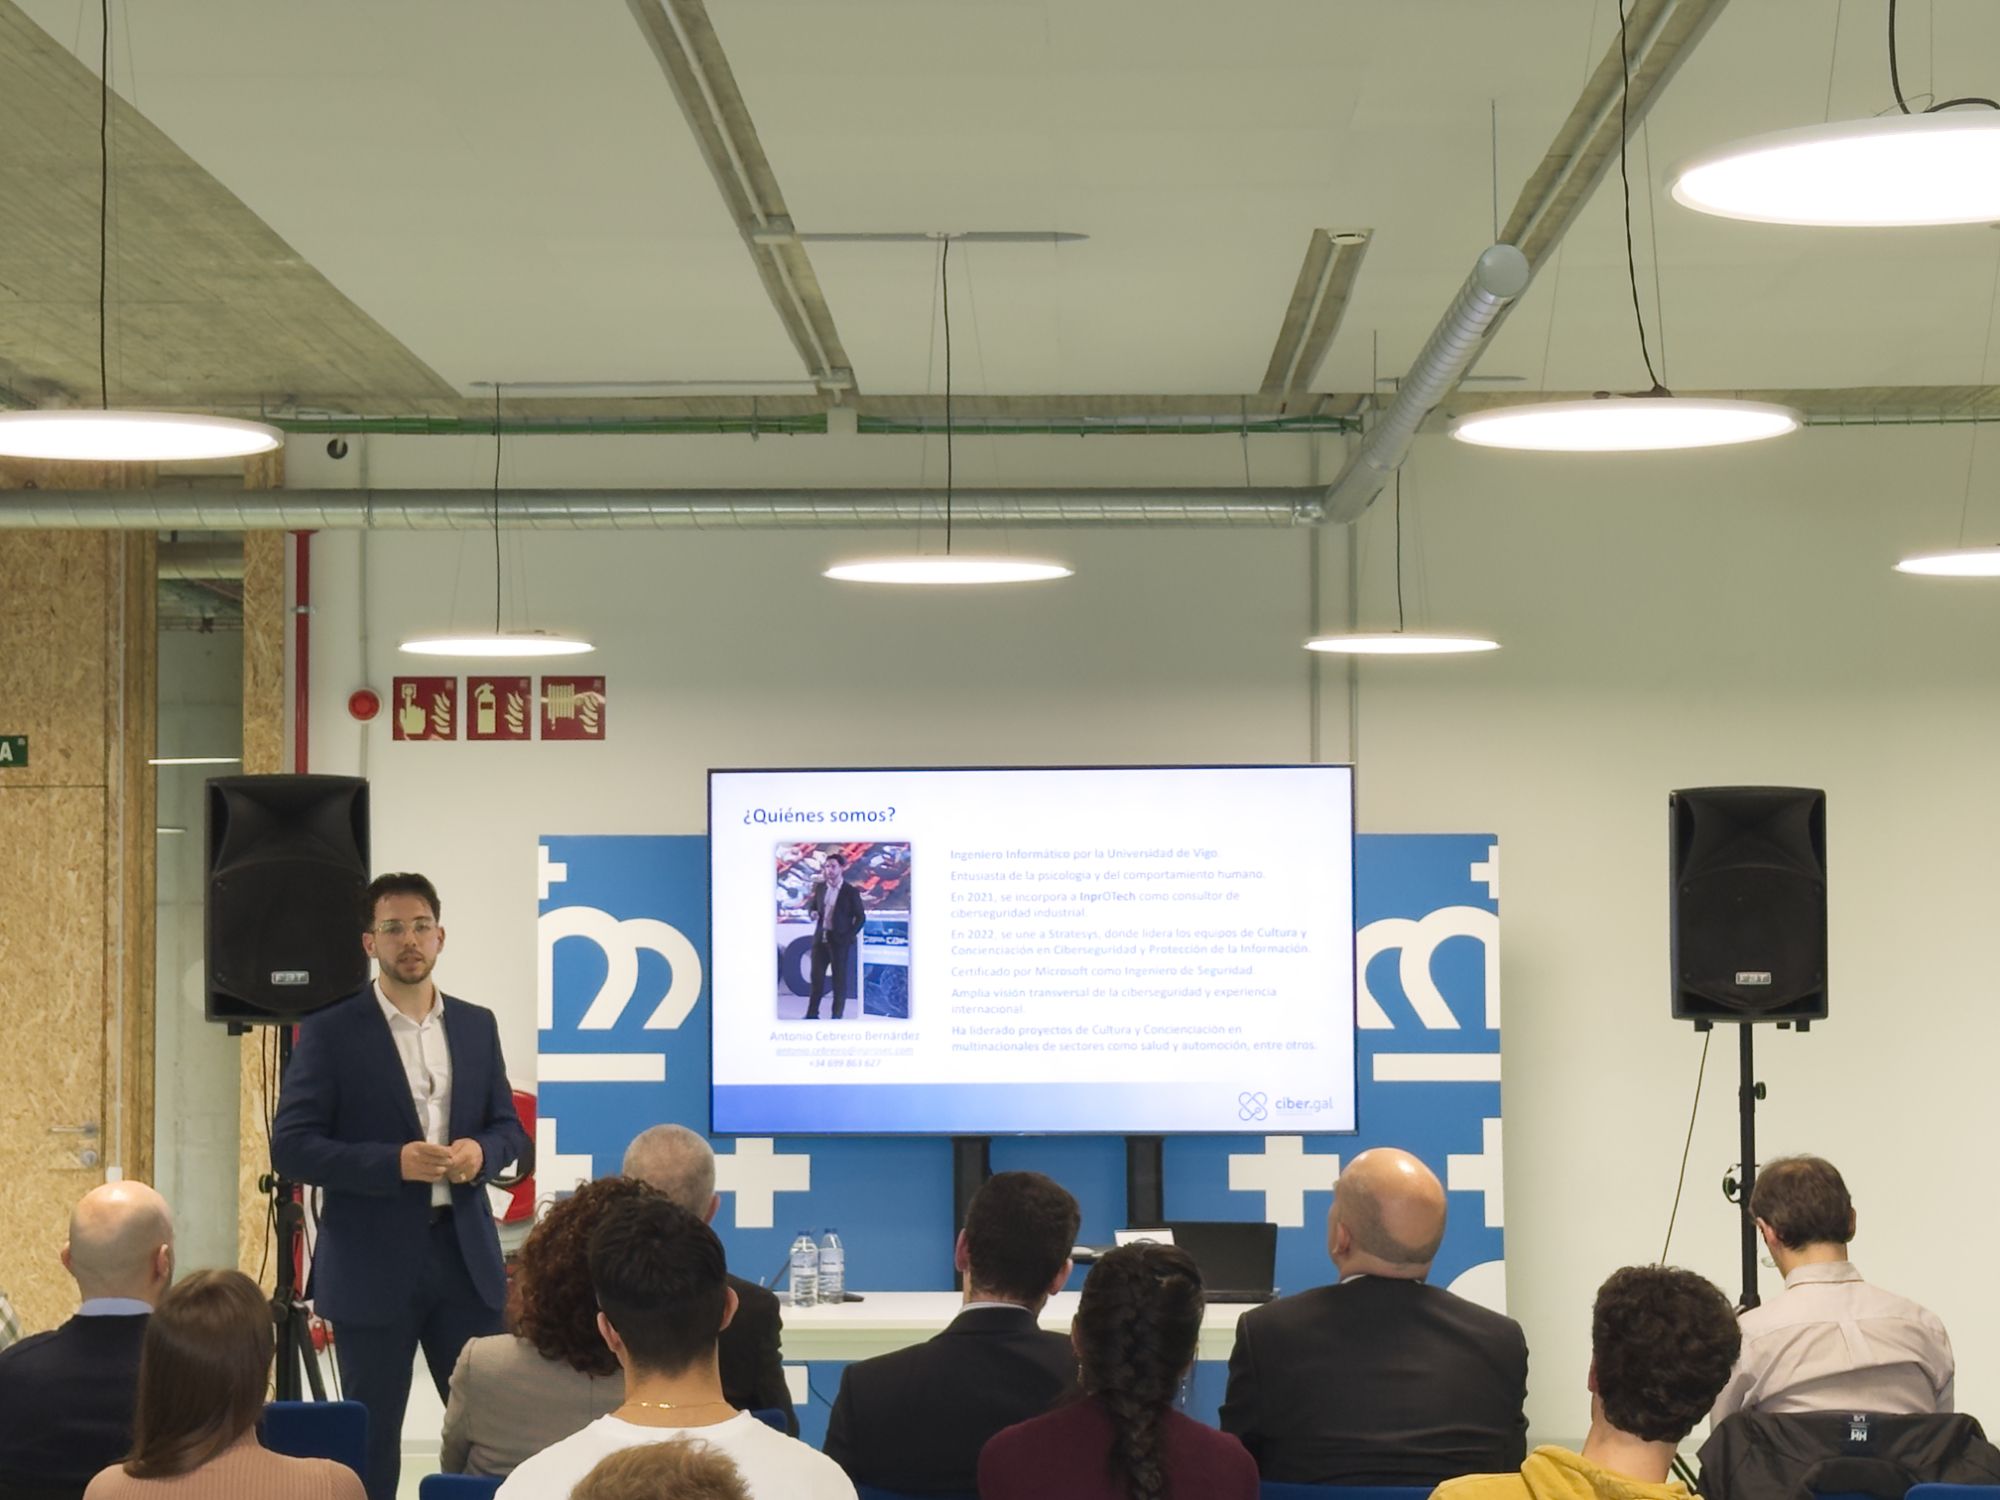
- CIBERGAL · The human factor as the first line of defence
- CECOCIB · Cybersecurity in industrial environments
- CNTG · Introduction to cybersecurity for executives
- ESEI · GDG · Cybersecurity 4.0: protecting tomorrow's industry
Techpaper: A strategy for preventing data leaks in Microsoft environments (in Spanish) →