
01
Strategy and compliance consulting
Security master plans and roadmaps aligned with your business. Readiness for ISO 27001, ENS and NIS2, with compliance that is understandable and actionable —not a box-ticking exercise.
I'm Antonio Cebreiro, an independent cybersecurity consultant. I help companies like yours comply with NIS2, ISO 27001 and ENS, get real value from the Microsoft 365 security they already pay for, and train their teams. You work directly with me, in plain language.
A personal reply within 24 business hours · No commitment
Pick the one closest to your day-to-day. If you recognise yourself in any of them, this is exactly the kind of work I do.
The directive is already in force and nobody in the company knows exactly what it demands or where to start. I clear that up and we turn it into a prioritised plan.
Many Entra, Purview, Defender and Intune capabilities may already be included in the licences you pay for. Properly configured, they deliver more security than most of the new tools you're being sold.
IT puts out fires, but nobody sets priorities or answers to management. That's the gap I fill, a few hours a month.
One employee's click can cost more than any technical failure. I train your workforce and your executives so that click never happens.
Most companies aren't short of technology: they're short of someone who will tell them plainly where to start and who to trust. That's what I do, freelance and remotely, for small and mid-sized companies.
Security master plans and roadmaps aligned with your business. Readiness for ISO 27001, ENS and NIS2, with compliance that is understandable and actionable —not a box-ticking exercise.
Training for technical teams, awareness for the whole workforce and cybersecurity for executives. Security culture programmes and talks that actually stick, backed by real social engineering experience.
For when you need to get into the detail and leave the technology up and running. I specialise in DLP and data loss prevention, email security, Microsoft ecosystem security and Zero Trust architectures. We start by squeezing the security capabilities you already pay for in your licences and hardly ever use.
If your company doesn't have —or doesn't yet need— a full-time security lead, I fill that gap from the outside: priorities, decisions and follow-up month by month. The industry calls it a vCISO, without the cost of a permanent hire.
No blind commitments: every step has a known format and you decide with all the information in front of you.
A free 30-minute call to understand your situation. You leave with an honest picture of where you stand, whether we end up working together or not.
If it makes sense to continue, you get a fixed proposal: scope, timeline and price. Priorities ordered by real risk, in a document your management can actually read.
We execute the plan together, at your pace: a one-off project or monthly follow-up, with me at the other end whenever something comes up.
Part of what I use with my clients is open to everyone: self-assessments and checklists you can use today, with no sign-up and without leaving your data anywhere.
Check whether your company falls under Directive (EU) 2022/2555 through Annexes I and II, assess 16 controls mapped to Articles 20, 21 and 23, and download a PDF report with your prioritised gaps.
Open the tool →
Pick the Microsoft 365 plan you have and instantly see which Microsoft Purview capabilities it covers and which are missing. Nineteen capabilities, nine plans, and for anything missing it tells you which plan unlocks it.
Open the tool →There is no email wall and no “leave us your details to see your result”. This is the deal, and you can verify it:
I'm a cybersecurity advisor, consultant and trainer. I help small and mid-sized companies protect what they've built: I define the strategy, sort out the priorities and train the people who keep it running.
I work freelance and remotely, with companies anywhere. That means dealing with me directly, with no middle layers and no product to sell you: my only interest is that you make the right decision.
I have built and led security teams from scratch, combining the technical and the strategic view. I'm an ISO 27001 lead auditor and AZ-500 certified in Azure security.
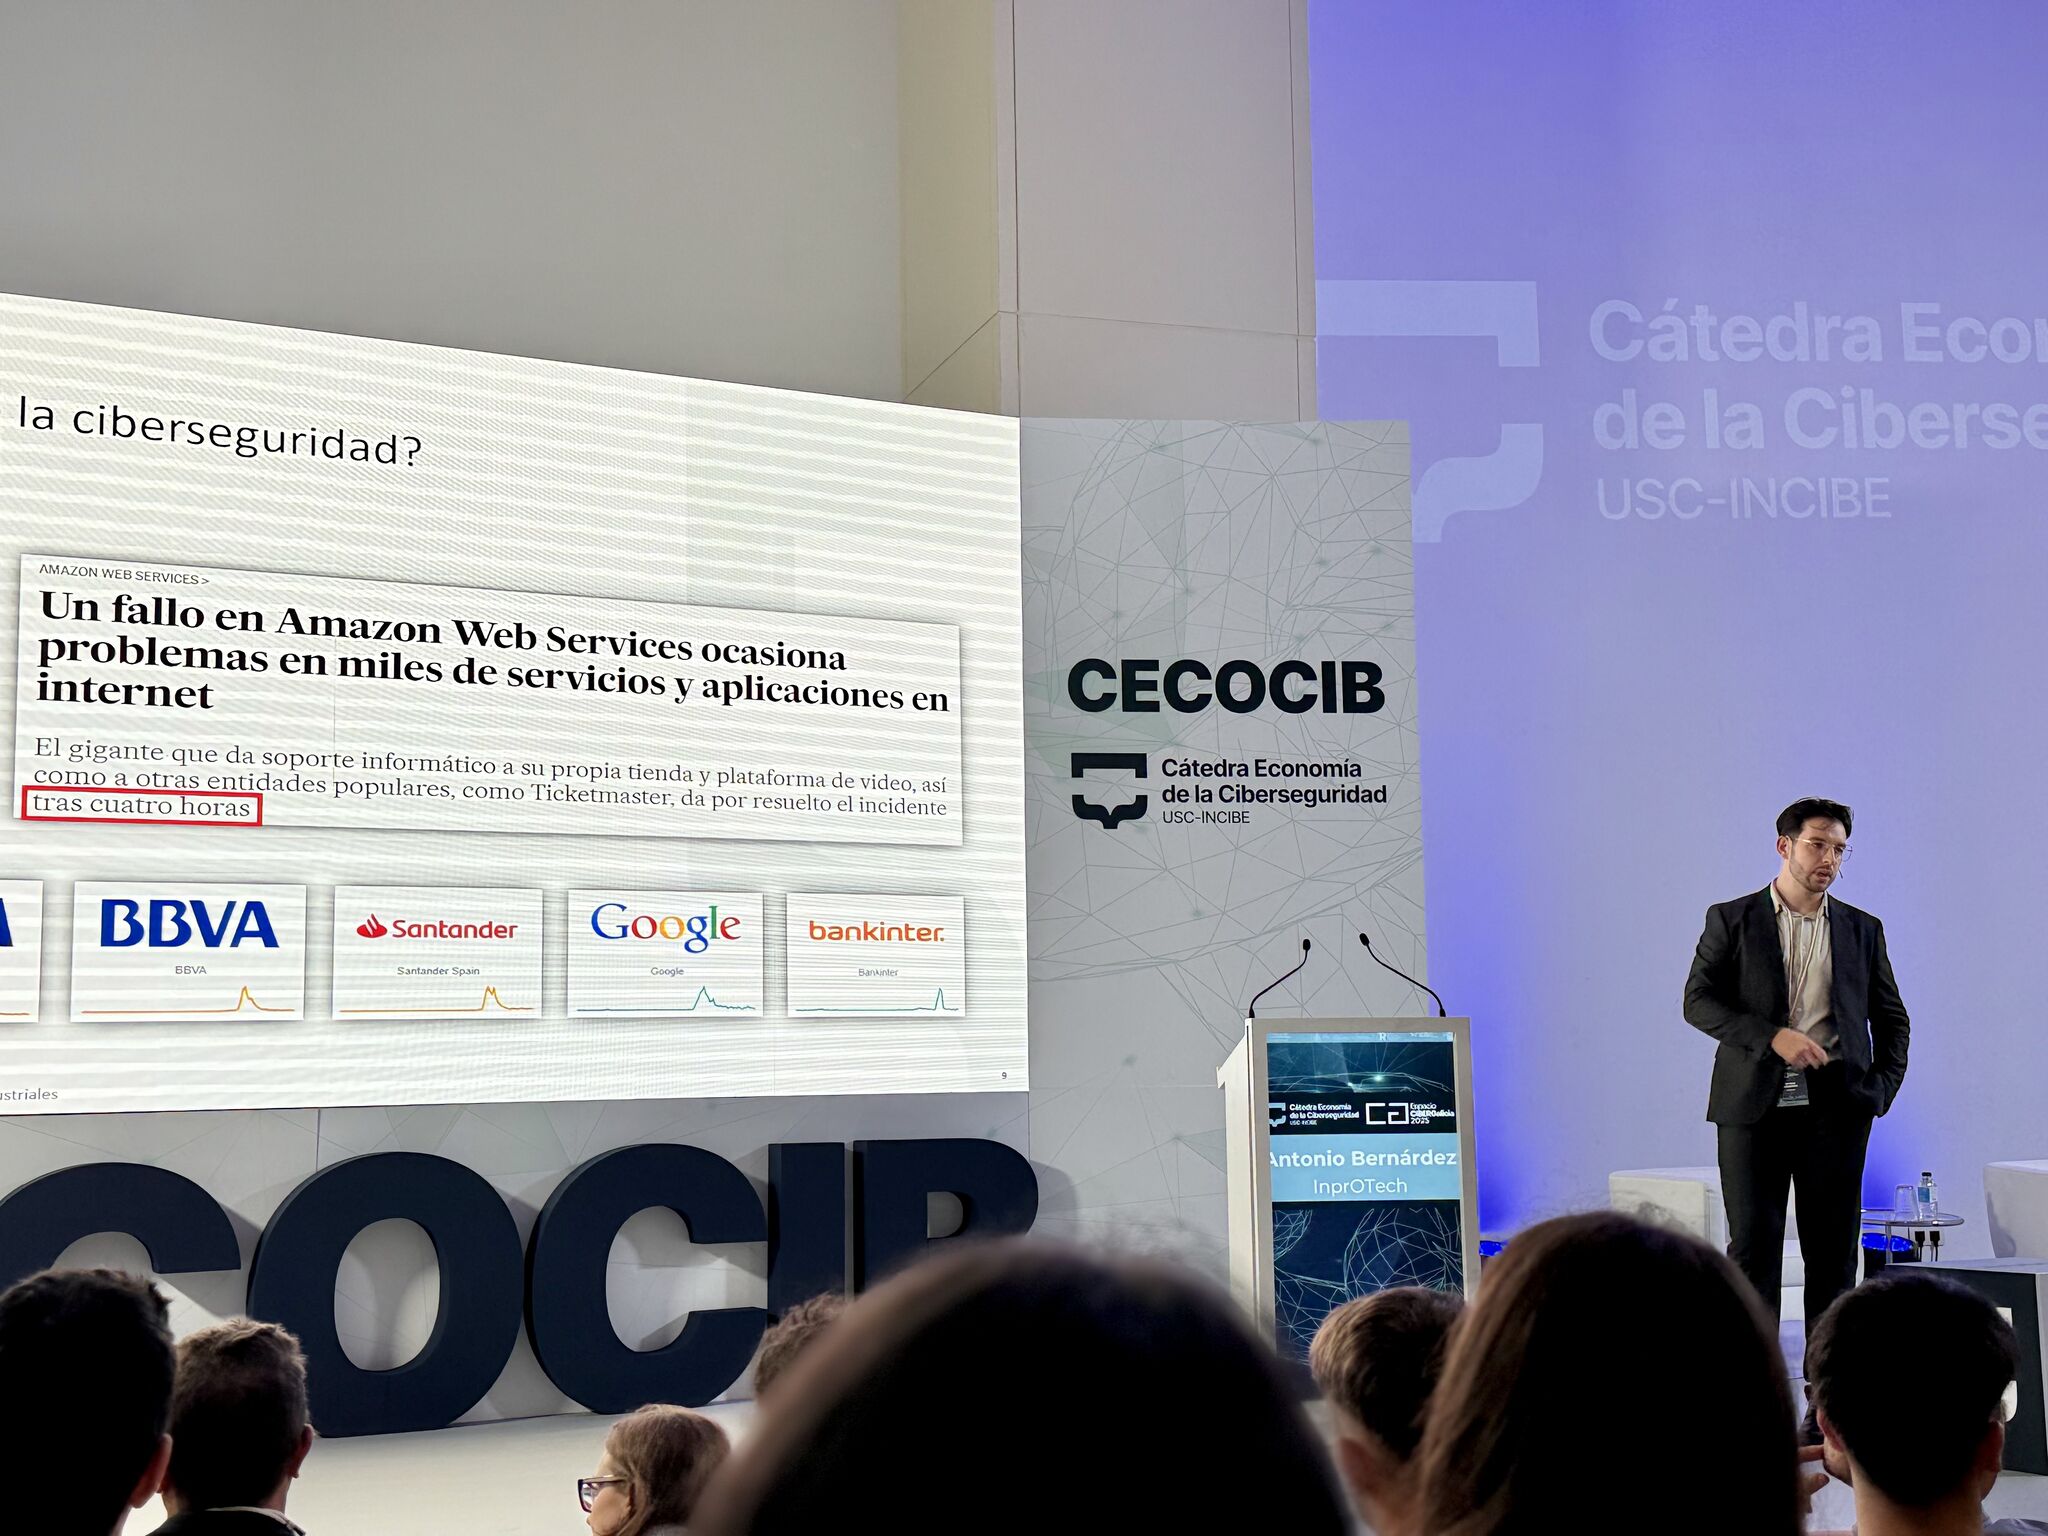 Speaking · industry event
Talks at industry events and universities, plus appearances on Galician television. Cybersecurity only protects you if it's understood.
Is your challenge about people rather than security? I am also a co-founder of Usoarit, a human resources consultancy for technology companies.
If you're looking for someone approachable and trustworthy to protect your company, tell me where you stand right now. I'll reply personally within 24 business hours.